
Secure by Design: How Webtonic Is Building AI Its Clients Can Trust
Over the past six months, Webtonic has been on a journey to ensure every prompt and every line of generated code is secure.
We have had great success with AI development tools such as GitHub Copilot and there is no debate that these tools have made our developers measurably faster. But We believed we needed to take a different approach when using AI in our Software Development Lifecycle(SDLC).
Treating AI tools with caution
Our relationships with our clients are founded in trust and when delivering applications for our clients we have access to their intellectual property (IP), which is often what makes their business unique.
To ensure that this trust is maintained, we follow rigorous recruitment process to ensure we recruit trustworthy, dependable and capable individuals. We also create an environment that supports secure work practices to ensure our and our clients best interests are secured.
When coding on a code base with AI tooling we are essentially bringing a third party into the loop. So, instead of asking our clients to trust a growing list of external vendors, we set out to bring the models to us.
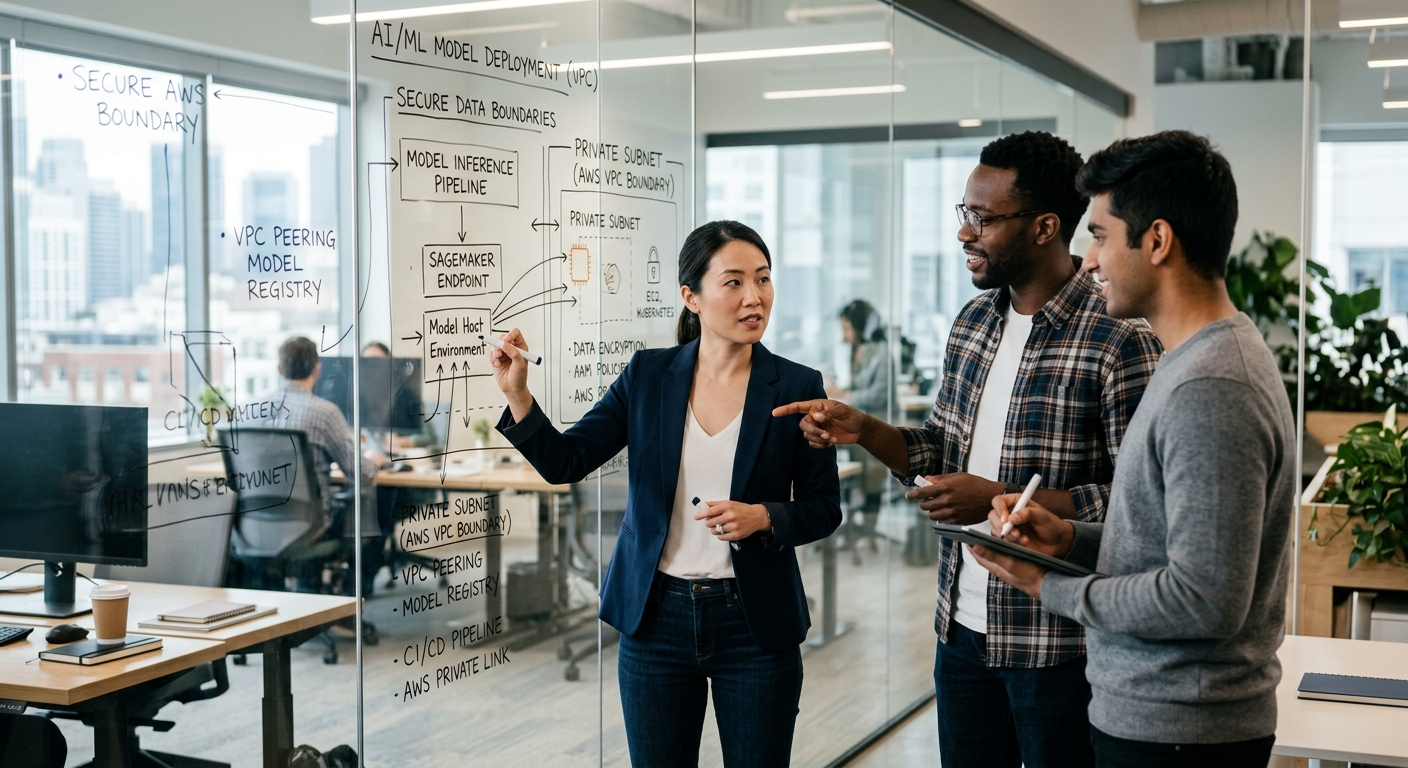
Bringing the models inside our AWS boundary
As AWS Advanced partner we have the expertise to host and manage our own models of choice. So we therefore made the decision to run our AI models on Amazon Bedrock, inside a dedicated AWS environment that Webtonic owns and governs. We still have access to leading models, but the difference is that these models are now under our control rather than a vendor’s.
In practice, this gives our clients four guarantees:
- No training on client data. Prompts and outputs are never used to train or improve the underlying models.
- Private traffic. Requests travel over private AWS network links, not the public internet, and stay in the region we choose.
- No loose API keys. Access runs through short-lived, role-based credentials.
- A full audit trail. Every model call is logged, so we can show who used AI, on what, and when.
Further to the above, we also have guardrails in place to protect personal information, credentials and NDA-protected materials. These types of data are filtered or anonymised before arriving at the model.
Secure AI across the whole SDLC
We didn’t want this initiative to only benefit the developers. Our goal was to create a secure set of tooling, connected to Bedrock, for all our capabilities.
The approach covers every discipline, not just code:
- Business analysts have the ability to draft user stories, acceptance criteria and API specifications directly from workshop notes.
- Designers can generate UX copy, accessibility annotations and developer handoff notes from Figma designs.
- Developers generate and/or refactor the code from the functional requirements
- QA engineers are able to generate test cases and automations scripts from the functional requirements.
Our goal is to use spec-driven development to tie the entire SDLC together. We believe we need to give the AI structured specifications, from which it can generate the code. The same specifications ultimately drive the design, the code and the tests, allowing for consistent and verifiable AI output. And we always have human in the loop reviews at each stage of the process.
Built by our teams, together
Building this has been a team effort across all our capabilities. Our AWS and AI leads are instrumental in building the platform and tooling to ensure that security was designed into the solution from the onset.
For our clients, the result is simple. They get the speed and quality benefits of AI on their projects, with clear answers about where their data goes and who can see it.
For Webtonic, this is how a team of 35 can deliver the output of a much larger one without compromising on the things we care about most: quality, reliability, security and user experience.